Conferences


The rise in ransomware and supply-chain attacks over recent years highlights the cybersecurity challenges facing society as perpetrators continue to evolve their tactics and techniques to evade risk-mitigation strategies. Though most cyber intrusions to date have been localised and associated costs relatively modest, the potential for a widespread cyber incident persists.
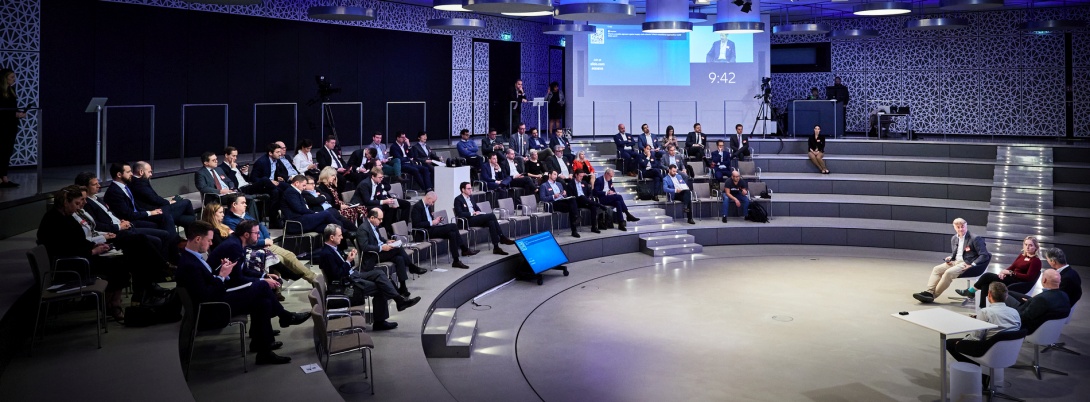
The Geneva Association's 2022 Cyber Conference explored how the cyber threat landscape is changing, how re/insurers are responding and where progress can be made to bolster the role of cyber insurance in building societal resilience.
Cyber is consistently ranked as a top global risk among business leaders, yet only a small fraction of related economic losses are currently insured. Insurers face challenges in boosting the take-up of cyber insurance, both on the supply side, such as quantifying and pricing accumulation risk, and on the demand side, including lack of awareness of the benefits of the product. However, they must work to help close this major protection gap if they are to retain their relevance in today’s digital world.
Although it may be natural to see cyber as a technical security issue, managing the associated risks is part of a broader sustainability agenda. Cyber resilience has links to the ‘E’, ‘S’ and ‘G’. For example, as we transition towards greener energy, safeguarding renewable energy infrastructure against both physical and cyber risks will become more important. Likewise, increased internet connectivity across societies puts additional emphasis on good cyber governance to protect individuals’ personal and private information.
There is clearly a huge opportunity for insurers in the cyber space but clarity around coverage and collaboration across the industry will be required to define effective insurance solutions to address growing cyber threats.
Daniel Trueman, Global Head of Cyber & Technology, AXIS Insurance, AXIS Capital; Harriet Gruen, Senior Cyber Risk Advisor, AXIS Capital; Alex Creswell, Strategic Advisor, Beazley; Jörg Schauff, VP Threat Advisory, QuoIntelligence; Ralf Schneider, Group CIO, Allianz
This panel discussed the evolving cyber threat landscape. Although ransomware has grabbed the headlines recently, this is just a part of broader, underlying shifts in the capabilities, behaviours and motivations of malicious actors. In particular, geopolitical tensions have spawned increased state-sponsored/-supported cyberattacks and allowed a whole cybercrime-as-a-service (CaaS) ecosystem to proliferate. CaaS has democratised offensive cybercriminal activity: hacking tools and services as well as stolen remote access credentials are bought, sold or loaned on the dark web, allowing even those with rudimentary IT skills to launch cyberattacks.
The ongoing Ukraine-Russia war has increased the threat of destructive cyberwarfare alongside disruptive, extortion and espionage attacks. So far, the conflict has yet to trigger major cyber spillovers to other countries. However, that could change as the kinetic war progresses, especially if Russia uses cyber activity to pressure Ukraine’s allies to support a negotiated settlement. The hacktivists supporting both sides of the war may also turn their attention back to corporate targets and the lucrative gains from cybercrime.
Companies therefore cannot rely solely on traditional cybersecurity defence tactics such as endpoint detection and response, even though they remain very important. While human mistakes are often an important feature of how cyberattacks propagate – for example, through email phishing campaigns – improved risk awareness and training will only go so far in boosting cyber resilience. Firms also need to get on the front foot and proactively search for cyber threats that are lurking undetected in their own networks and digital supply chains. Machine-learning tools can help to uncover cybersecurity vulnerabilities and intrusions, but firms must interpret the signals from those predictive models carefully given the potential for false positives.
State-sponsored hostile cyber activity presents a challenge not only for targeted households and firms but also for re/insurers who assume some of the associated risks, either through affirmative policies or as part of traditional property and casualty insurance. Losses linked to wars are generally not insurable, but attributing cyberattacks to nation states is difficult. Even if the technical characteristics of an incident have all the hallmarks of a particular perpetrator, proving they acted under the control or direction of a sovereign state is hard. Efforts by the re/insurance industry to align policy language with modern cybersecurity threats and create greater contract clarity are laudable, not least to avoid any reputational damage surrounding disputed coverage after an event. But contract certainty is not the same as legal certainty, and attribution will continue to be the subject of intense legal arguments, both in domestic and international courts.
Matt Prevost (on screen), Senior Vice President, Chubb; Simon Dejung, Chief Underwriting Officer Cyber Reinsurance, SCOR; Peter Hacker, Founder & Director, Distinction.Global; Helga Munger, Senior Claims Manager, Munich Re; Tom Johansmeyer, Head of Property Claim Services (PCS), Verisk; Chuck Jainchill, Cyber Product Development Leader, AIG
To expand the cyber insurance market sustainably, new risk-absorbing capital will be needed to match the ballooning growth in exposures. Fundamental to that is robust contract design that gives re/insurers and prospective capital investors comfort that the assumed risks are manageable. Arguably, contract wordings failed to keep pace with risk exposure during the soft underwriting market of 2015–2019. The panel debated recent market initiatives to refine policy language and how far they are likely to deliver increased legal certainty over coverage.
Various proposals put forward by market practitioners offer improvements to contract templates, not least the increased precision over the nature of assets protected and the types of attack to which the policy will respond. However, the different terminology used for ostensibly similar concepts could be confusing. Moreover, the new policy terms would likely still face legal challenges in the event of a major cyber incident, especially over the definition of critical infrastructure, what amounts to a major detrimental impact and attributing any hostile attack to a particular nation state.
Beyond exclusions and endorsements, other product innovation will also be important. This includes further developments in excess-of-loss cyber reinsurance and industry loss warrants that allow capital providers with different risk appetites to participate, thereby boosting overall capacity in the market.
Cyber insurance is relatively new but it has evolved rapidly from providing protection largely against liability to third parties for loss or corruption of data. Most recent insured claims have been first-party losses, including business interruption and remediation expenses arising from ransomware. Cyber insurance is also no longer solely a risk transfer product. Insurers increasingly offer ancillary risk prevention/mitigation services alongside loss indemnification, often in partnership with others in the cybersecurity ecosystem.
However, re/insurers can only absorb risks from policyholders if they are adequately rewarded for the capital they hold to cover unexpected losses. While claims thus far have been largely attritional, the potential for a cyber catastrophe is ever present and the cost of cyber insurance must reflect that. Arguably, the recent upwards correction in cyber pricing may need to go further to properly recognise the intrinsic cat element of cyber, even if the frequency of attritional claims continues to fall.
The learnings and insight from incidents will help to increase our understanding and ability to model the risk, which will encourage more re/insurers into the market. The re/insurance sector alone, however, does not have the balance sheet capacity to cover all cyber risks, so other private market capital will be needed. Innovation in the way cyber risk instruments are structured will help to align exposures with capital market investors’ risk appetite. Thought should also be given to the potential role of a public-private partnership for cyber, which, if well-designed, could further catalyse participation in the cyber insurance market and expand risk-absorbing capacity.
Shannan Fort, Partner – Financial, Cyber, McGill and Partner; Kyle Bryant, International Chief Underwriting Officer, Resilience Insurance; Aidan Flynn, Head of London and International Underwriting Management, Beazley; Jürgen Reinhart, Chief Underwriter Cyber, Munich Re; Marek Stanislawski, Global Cyber Underwriting Lead, Allianz Global Corporate & Specialty
The sharp rise in cyber loss ratios over recent years, on the back of elevated ransomware claims, has triggered not only a correction in pricing but also a tightening in underwriting practices. Rudimentary questionnaires have been replaced by more detailed scrutiny of insureds’ cybersecurity standards and protocols, including the use of outside-in scanning to identify vulnerabilities. This has helped improve policyholders’ security postures, which hopefully will reduce the frequency and severity of future claims.
In light of recent market developments, the panel discussed ongoing initiatives to lock in permanently those procedural gains in underwriting and improve the predictability of cyber losses. Ingesting data about an insureds’ cyber hygiene solely at policy inception is seldom sufficient. Ongoing innovations in underwriting will require increased collaboration with policyholders to capture almost real-time data that can generate insights about their changing risk profile over time. Insureds will be more likely to engage if they are incentivised to share information, not only through premium discounts or higher policy limits but also demonstrable evidence that the relationship with their insurer improves the return on their cybersecurity investments.
Insurtechs and managing general agents have paved the way in leveraging technology to implement automated, data-augmented decision-making about evolving cyber threats and assist their policyholders to resist and/or recover from cyber intrusions. This is especially true for small and medium-sized enterprises, who often lack the resources to employ best-practice security protocols. Traditional insurance carriers are embracing similar approaches to further upgrade their underwriting practices and better understand their insureds’ cyber risks.
Kerstin Awiszus (on screen), Professor of Mathematics, University of Applied Sciences and Arts, Hannover; Eric Durand, Head Cyber Centre of Competence, Swiss Re; Rory Egan, Head of Cyber Analytics, Reinsurance Solutions, Aon; Andreas Kempe, Cyber Actuary, Tokio Marine; Justyna Pikinska, Global Head of Cyber Analytics, Gallagher Re; Jamie Pocock, Head of Cyber Analytics – International, Guy Carpenter
A key issue for cyber re/insurers is the potential for incident losses to accumulate across policyholders and geographies. Unlike for natural catastrophes, there are few, if any, historical episodes of such extreme cyber losses to help inform about the scale and likelihood of such events. While counterfactual analysis of past incidents can help simulate what a cyber catastrophe might look like, the past may not always be a good guide to the future. Cyber is a dynamic risk and depends significantly on shifts in the motivations and capabilities of attackers and the robustness of cyber defences.
The panel discussed the evolution and use of formal cyber accumulation risk models. These have developed significantly over recent years and are now integral to how re/insurers evaluate and manage their cyber insurance portfolios. With improved data capture and standardisation, such models will no doubt further improve our understanding of the key risk drivers, including the ways in which losses can aggregate. However, it is important to remember that the models are subject to considerable uncertainty – the full set of future extreme scenarios is unknowable and the parameters that calibrate the estimated losses are unavoidably imprecise. Moreover, there are certain incidents such as cyberwarfare that are so complex they are practically impossible to model, making them uninsurable.